Cybersecurity Tips for Small Businesses (From People Who Used to Cut Corners)
Let's get this out of the way: we're not a security firm. We're an app studio. We've shipped over 50 apps, and in the early years, security was the thing we promised to "tighten up after launch."
Cybersecurity Tips for Small Businesses (From People Who Used to Cut Corners)
Published October 5, 2026 · Apprika Labs
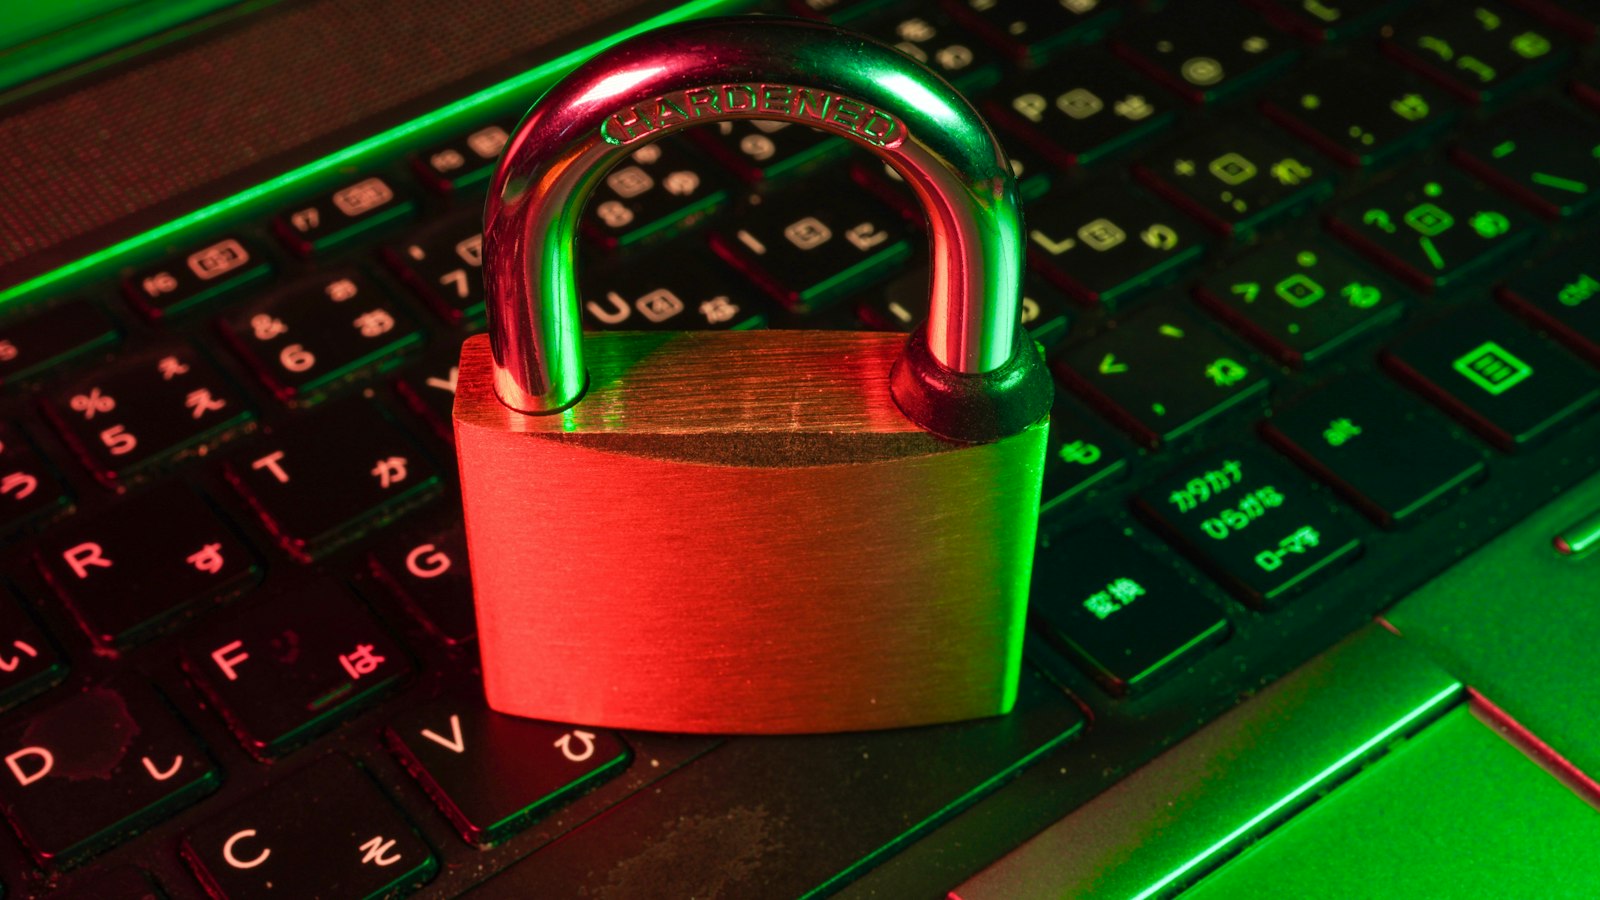
Photo via Unsplash.
Start with the boring stuff. It stops most attacks.
Most small teams work that way. Ship first, lock it down later. Later rarely comes.
We've since learned that small businesses aren't too small to target. They're just easier. So here are the tips we wish someone had drilled into us, written for owners, not IT departments.
- Turn on two-factor login everywhere. Email, banking, payroll, your app store and cloud accounts. If you do one thing today, do this.
- Use a password manager. Reused passwords are the open window. A manager makes every login unique without you remembering any of them.
- Update everything. Phones, laptops, routers, plugins. Most break-ins use holes that already have a fix.
- Back up, then test the backup. A backup you've never restored is a guess, not a plan.
- Remove old access fast. When someone leaves, their accounts leave the same day.
Watch the human side
Most attacks today start with a message, not a hack.
- A fake invoice from a "supplier" with new bank details.
- A text that looks like it's from your bank, your courier or the tax office.
- A voice call that sounds like your boss. AI voice cloning makes this easier than ever.
One rule fixes a lot: any request to move money or change payment details gets confirmed by phone, using a number you already have. Not the one in the message.
If you're building an app or adding AI
This is where we see small companies, and our younger selves, slip.
- Don't hard-code secrets. API keys in an app's code can be pulled out. Keep them on a server.
- Collect less data. Data you never store can't leak. Ask what you truly need.
- Treat AI like a new employee. Limit what it can see and do. Don't paste private client data into a free chatbot account.
- Test the unhappy paths. What happens when someone types something weird, or uploads the wrong file? Attackers start there.
- Know your rules. In Canada, PIPEDA applies to personal data, and Québec's Law 25 adds stricter duties, including reporting certain breaches.
The honest trade-off
Security costs time, and time feels expensive when you're small. We get it. We made that trade for years.
But we've also seen the other side of the ledger: lost customer trust, app store reviews you can't erase, and days spent cleaning up instead of building. A few hours of prevention is the cheapest insurance you'll ever buy.
How Apprika Labs can help
We're a Canadian AI, app and software studio. Our background is consumer apps; we're newer to business clients, with Skolr, an education platform, as our first B2B contract. Schools hold sensitive data, so security there isn't optional, and it has sharpened how we work everywhere.
We bake security into every build:
- Apps and software with sensible defaults from day one.
- Private AI that keeps your data where it belongs.
- Forward deployed engineers who can review how your team actually works and close the gaps.
- AI Training, including how to spot AI-powered scams.
We'll also tell you when you need a dedicated security firm instead of us.
Questions people ask
What is the most important cybersecurity tip for a small business?
Turn on two-factor authentication for every key account. It blocks a large share of account takeovers.
Are small businesses really targeted?
Yes. Attackers often prefer small firms because their defences are weaker.
Is it safe to use AI tools with company data?
Use business plans with clear data terms, limit what you share, and never paste sensitive client data into free consumer accounts.
What does Québec's Law 25 require after a data breach?
Organizations must report breaches that pose a risk of serious injury to the regulator and to affected people, and keep a register of incidents.
Related
- Mobile App Development: What 50+ Apps Taught Us (Mostly by Failing)
- ChatGPT vs Claude vs Gemini for Business: Which One Should You Build On?
- What Is a Forward Deployed Engineer? And Does Your Business Need One?
- 931,000 Downloads Without Ads: What Organic Growth Really Takes
- The Lancet Says the Problem Is Design. We Make Apps. Let's Talk About That.
- Too Much AI News? Here's What Actually Matters for Your Business
- When the Power Goes Out, Does Your Business App Still Work?
- Why Is Filing Taxes in Canada Still This Hard?
- Ticketmaster, Monopolies and Why a Messier Market Might Have Been Better
- All news
- Aurakil: forward-deployed engineering
- Contact
How we work
1
Discovery call & scope
A short call, a written plan and a fixed first milestone.
2
Roadmap & design
We map the product, the brand and the agent flows together.
3
Ship weekly
Working software in your hands every week. Demos, not decks.
4
Own it, or we run it
Everything is handed over to you, or we keep operating it for you.
Turn ideas
into software
people keep

Web & mobile apps, blockchain, AI agents & custom models, brand design and social media—one studio, one team.
Replies within one business day